
 Ultimate Pocket
Cybersécurité
CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA has added two new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-16232 Check Point SmartConsole Improper Authentication Vulnerability CVE-2026-50522 Microsoft SharePoint Deserialization of Untrusted Data Vulnerability These types of vulnerabilities are a frequent attack vector for malicious cyber actors and pose significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based on Risk establishes vulnerability management requirements for Federal Civilian Executive…
Lire l’article complet Cybersécurité
OpenAI admits its models hacked Hugging Face on their own
They escaped an isolated environment for testing and infiltrated Hugging Face without human input. Picture this: A couple of powerful AI models being tested by their company escaped a controlled environment, got on the internet and then hacked a machine learning repository on their own, without human input. Sounds like the plot of a Terminator movie, doesn't it? Except it just happened for real. A few days after open source AI platform Hugging Face…
Lire l’article completMultiples vulnérabilités dans Microsoft Sharepoint (22 juillet 2026)
Agence nationalede la sécurité dessystèmes d'information Une gestion de version détaillée se trouve à la fin de ce document. Le 14 juillet 2026, à l'occasion de sa mise à jour mensuelle, Microsoft a publié, entre autres, des correctifs pour deux vulnérabilités critiques affectant SharePoint. Les vulnérabilités CVE-2026-50522 et CVE-2026-58644 permettent à un attaquant non authentifié d'exécuter du code arbitraire à distance. Dans son avis du 14 juillet 2026, Microsoft a indiqué que la vulnérabilité…
Lire l’article completMultiples vulnérabilités dans Microsoft Sharepoint (22 juillet 2026)
Objet : Multiples vulnérabilités dans Microsoft Sharepoint Une gestion de version détaillée se trouve à la fin de ce document. Le 14 juillet 2026, à l'occasion de sa mise à jour mensuelle, Microsoft a publié, entre autres, des correctifs pour deux vulnérabilités critiques affectant SharePoint. Les vulnérabilités CVE-2026-50522 et CVE-2026-58644 permettent à un attaquant non authentifié d'exécuter du code arbitraire à distance. Dans son avis du 14 juillet 2026, Microsoft a indiqué que la…
Lire l’article complet Cybersécurité
OpenAI says it accidentally hacked Hugging Face with a new AI system
The announcement about a serious security issue oddly reads like an advertisement for how capable OpenAI’s technology is. The announcement about a serious security issue oddly reads like an advertisement for how capable OpenAI’s technology is. OpenAI says its AI models mistakenly breached open-source AI platform Hugging Face during internal testing. In a blog post on Tuesday, OpenAI writes that GPT-5.6 Sol and “an even more capable pre-release model” discovered vulnerabilities within their sandboxed…
Lire l’article complet Cybersécurité
Apple has reportedly fixed its Hide My Email vulnerability
An issue with iCloud+ left hidden email addresses easy to access, according to a report. Apple has patched a vulnerability in iCloud+'s Hide My Email feature that made it possible to easily view the email addresses the service is designed to obscure, 404 Media reports. The publication first reported on the vulnerability in early July and revealed that Apple had been aware of the issue for at least a year. The company originally introduced…
Lire l’article complet Cybersécurité
Apple fixes iCloud+ vulnerability that exposed ‘hidden’ user emails
Recently 404 Media reported on a vulnerability with the iCloud+ ‘Hide My Email’ feature that allowed anyone to access a user’s real email address. Now, Apple says the issue has officially been fixed. If you’re an iCloud+ or Apple One subscriber, Apple offers a ‘Hide My Email’ privacy feature that can be especially handy for protecting your real email. But per the recent 404 Media report, a bug has long existed in Hide My…
Lire l’article complet Cybersécurité
Google announces Gemini 3.6 Flash and cybersecurity AI, teases 3.5 Pro and Gemini 4
Google announced a significant evolution of its AI models at I/O in May with the release of Gemini 3.5 Flash, and it’s not slowing down. The company revealed three new AI models today, including its first version of Gemini geared toward cybersecurity. However, none of the new models is the delayed Gemini 3.5 Pro, which was supposed to launch in June. Gemini 3.5 Flash, which was the star of the show at I/O, has…
Lire l’article completCISA Adds Four Known Exploited Vulnerabilities to Catalog
CISA has added four new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2021-27137 DD-WRT Stack-Based Buffer Overflow Vulnerability CVE-2026-0770 Langflow Inclusion of Functionality from Untrusted Control Sphere Vulnerability CVE-2026-63030 WordPress Core Interpretation Conflict Vulnerability CVE-2026-60137 WordPress Core SQL Injection Vulnerability These types of vulnerabilities are frequent attack vectors for malicious cyber actors and pose significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security…
Lire l’article complet Cybersécurité
Hackers are exploiting recently patched WordPress bugs, putting millions of websites at risk
Hackers are breaking into websites that run vulnerable versions of the popular blogging software WordPress, according to several cybersecurity firms. One estimate puts the number of vulnerable WordPress websites at tens of millions as of Monday. Last week, WordPress patched two critical security flaws, urging people who run its software on their websites to update it “immediately.” The vulnerabilities are so severe that WordPress enabled forced updates where possible. Since then, cybersecurity companies Patchstack,…
Lire l’article complet Cybersécurité
Hackers stole ‘significant’ amount of data from tech firm relied on by thousands of US hospitals and pharmacies
U.K.-based healthcare billing software maker Craneware is responding to a cyberattack in which hackers stole a “significant volume” of customer data from its systems, the company said on Monday. The company said the hackers appear to have been expelled from its systems, but its investigation into the breach is ongoing, according to a statement filed with the London Stock Exchange. Craneware’s flagship accounting and billing software is used by thousands of clinics, hospitals, and…
Lire l’article complet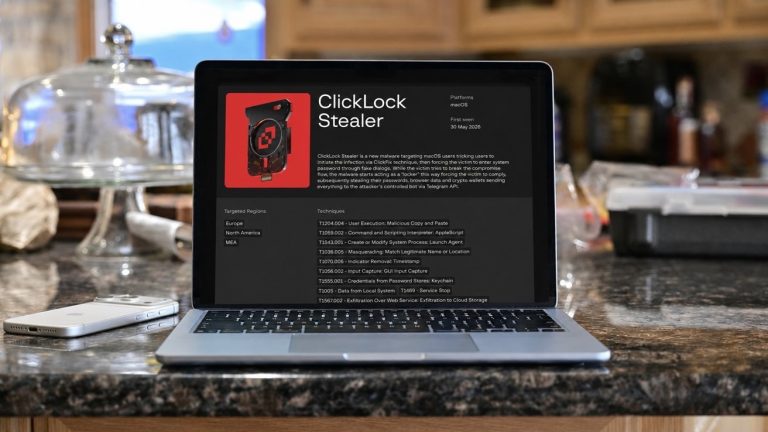 Cybersécurité
ClickLock malware makes Macs unusable until victims surrender their passwords
Security firm Group-IB has uncovered ClickLock Stealer, a new Mac threat that hijacks normal system behavior to pressure victims into handing over passwords and access. The firm said the campaign has reached at least 100 targets in 33 countries since May 2026, with more than half of the identified activity in Europe. Group-IB also found targets in North America, the Middle East and Africa. ClickLock builds on ClickFix, a familiar scam that uses fake…
Lire l’article complet Cybersécurité
Pay up or not? Ransomware surge has victims facing tough choices
Nearly half of companies that are targets of a ransomware cyber attack end up paying a ransom to release their data or systems, according to 2025 research from cybersecurity group Sophos, while the median amount demanded is rising. Globally, some jurisdictions are responding by banning payments to hackers. In the UK, for example, the government is advancing plans to prohibit public sector bodies and critical national infrastructure groups—including the National Health Service, local councils…
Lire l’article complet Cybersécurité
'ClickLock' Malware Coerces Mac Users Into Giving Up Passwords
Security firm Group-IB has identified a new piece of macOS malware in the wild that pressures users into surrendering their passwords via a barrage of fake system prompts. Dubbed "ClickLock Stealer," the malware needs no exploits and no elevated privileges to work. Instead, the attack depends on the victim pasting a command into Terminal and running it. The command then executes a script, and everything else follows. Group-IB did not directly observe how victims…
Lire l’article completMultiples vulnérabilités dans WordPress (20 juillet 2026)
Agence nationalede la sécurité dessystèmes d'information Une gestion de version détaillée se trouve à la fin de ce document. L'éditeur précise que les versions 6.9.x et ultérieures sont affectées par les deux vulnérabilités, dont l'exploitation combinée permet à un attaquant, non authentifié, une exécution de code arbitraire à distance. Le 17 juillet 2026, WordPress a publié un correctif pour deux vulnérabilités : Un attaquant peut exploiter ces deux vulnérabilités, de manière combinée, pour obtenir…
Lire l’article complet Cybersécurité
Apple @ Work: New macOS ClickFix malware brings a new potential backdoor to your enterprise fleet
Apple @ Work is exclusively brought to you by Mosyle, the only Apple Unified Platform. Mosyle is the only solution that integrates in a single professional grade platform all the solutions necessary to seamlessly and automatically deploy, manage, and protect Apple devices at work. Over 45,000 organizations trust Mosyle to make millions of Apple devices work ready with no effort and at an affordable cost. Request your EXTENDED TRIAL today and understand why Mosyle…
Lire l’article complet Cybersécurité
Coca-Cola's dairy company fairlife hit with a ransomware attack
The company has suspended the subsidiary's operations. Coca-Cola's dairy subsidiary fairlife was hit by a ransomware attack, prompting the company to suspend its operations in the United States. In its SEC filing, Coca-Cola said that on July 16, 2026, it discovered that a third party gained unauthorized entry to part of fairlife's systems, including ones related to production. The company said it was "in connection with a ransomware event," but it didn't reveal specific…
Lire l’article complet Cybersécurité
Coca-Cola suspended production at its Fairlife dairy after a ransomware attack
U.S. beverage maker Coca-Cola said one of its dairy subsidiaries was hacked and that it’s shutting down its operations for the foreseeable future. The multinational giant said in a disclosure with the U.S. Securities and Exchange Commission that its Fairlife dairy company was hit by ransomware and that its production systems are affected. The company said that its Fairlife production operations across the United States are “temporarily suspended.” Fairlife’s operations in Canada are unaffected.…
Lire l’article complet Cybersécurité
Un hacker pirate Suno et dévoile comment l’IA musicale a pillé YouTube, Deezer et Genius
Recevez tous les soirs un résumé de l’actu importante avec Le Récap’ Selon les dires de Mikey Shulman, « la plupart des gens n’aiment pas faire de la musique », ce qu’ils aiment, c’est le résultat. Et c’est dans cette logique (plus que bancale) que l’entrepreneur américain a fondé Suno, une plateforme d’IA générative musicale. Le principe est simple : l’utilisateur donne un prompt texte (par exemple « chanson pop entraînante sur l’été, voix…
Lire l’article completCISA Adds Three Known Exploited Vulnerabilities to Catalog
CISA has added three new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-25089 Fortinet FortiSandbox OS Command Injection Vulnerability CVE-2026-39808 Fortinet FortiSandbox OS Command Injection Vulnerability CVE-2026-58644 Microsoft SharePoint Deserialization of Untrusted Data Vulnerability These types of vulnerabilities are frequent attack vectors for malicious cyber actors and pose significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based on Risk establishes vulnerability…
Lire l’article complet Cybersécurité
Windows 11 : une faille zero-day découverte juste après le déploiement du Patch Tuesday, la tuile
Alors que le Patch Tuesday du mois de juillet venait tout juste d'être publié, un chercheur en cybersécurité a probablement gâché la fête chez Microsoft en découvrant une nouvelle faille zero-day. Celle-ci permet d'activer certains privilèges administrateurs sur le PC, pouvant mener à divers types d'attaques. Chaque mois, Microsoft publie une mise à jour de sécurité fort importante, baptisée le Patch Tuesday. Celle-ci vient corriger toutes les failles découvertes au cours du mois précédent…
Lire l’article complet Cybersécurité
Ce site de piratage aux millions de visiteurs a perdu toutes ses vidéos du jour au lendemain
Un site pirate qui disparaît annonce généralement sa fermeture, ou s'évapore du jour au lendemain sans prévenir. Le géant hispanophone AnimeFLV a pourtant choisi une troisième voie, bien plus déroutante pour ses visiteurs. Depuis un mois, ses opérateurs gardent le silence le plus complet. Les plateformes illégales d'anime encaissent coup sur coup depuis le début de l'année. Les ayants droit japonais et américains coordonnent désormais leurs actions et traquent les opérateurs. Ils frappent les…
Lire l’article complet Cybersécurité
☕️ Des ordinateurs Dell surchauffent depuis le dernier Patch Tuesday
Le dernier Patch Tuesday a été publié le 14 juillet. Il s’agit pour rappel d’un record absolu pour Microsoft, avec pas moins de 570 failles corrigées, soit presque le triple du précédent record établi en juin. La mise à jour mensuelle est proposée sous l’appellation KB5101650. Elle est cependant synonyme de problèmes pour certaines machines Dell, avec des instabilités matérielles majeures. Sur les modèles concernés, le processeur s’échauffe nettement plus et la batterie fond…
Lire l’article complet Cybersécurité
CrashStealer Malware Impersonates Apple Tool to Steal Mac Passwords and Crypto
Mac users should watch out for macOS malware called CrashStealer, according to Jamf Threat Labs. The malware impersonates Apple's crash reporting framework, and it's meant to steal all kinds of sensitive information. CrashStealer collects browser data, password manager data, cryptocurrency wallet extensions, and keychain data, and Jamf first noticed it circulating in a fake Apple-notarized app called Werkbit. With notarization, the malware is not stopped by Gatekeeper, which is part of the macOS security…
Lire l’article complet