
 Ultimate Pocket
Cybersécurité
 Cybersécurité
Meet GPT-Red: an LLM super-hacker OpenAI built to make its models safer
OpenAI has built an LLM super-hacker called GPT-Red that it uses as a sparring partner to help its other models boost their defenses against cyberattacks. Last week the company released the latest version of its flagship LLM, GPT-5.6. OpenAI says that training it against GPT-Red made the model its most robust release yet. GPT-Red automates a type of safety evaluation for software systems known as red-teaming, which is typically done by a team of…
Lire l’article complet Cybersécurité
A hacker accessed Suno source code that reportedly details how the company scraped millions of songs
The company says it was breached in November and "no sensitive personal information was compromised." Suno — an app that vomits out soulless audio in the form of AI-generated "music" — has been hacked. According to 404 Media, the hacker accessed data related to Suno's training practices, as well as details on its customers. It's not exactly a secret at this point that copyrighted music has been used for AI training. Last month, The…
Lire l’article completCISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA has added two new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2023-4346 KNX Association KNX Protocol Connection Authorization Option 1 Overly Restrictive Account Lockout Mechanism Vulnerability CVE-2026-46817 Oracle E-Business Suite Improper Privilege Management Vulnerability These types of vulnerabilities are frequent attack vectors for malicious cyber actors and pose significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based on Risk establishes…
Lire l’article complet Cybersécurité
☕️ Un Patch Tuesday record pour Windows : 570 failles colmatées, dont deux déjà exploitées
En juin, Microsoft avait déjà battu son record avec 200 failles corrigées. Entre temps, l’éditeur a expliqué comment l’intelligence artificielle faisait désormais partie de ses processus de révision. Il fallait donc s’attendre à une déferlante de correctifs dans les mois qui suivraient, avant sans doute de retomber sur un rythme de croisière. Microsoft officialise son utilisation intensive de l’IA pour la découverte des failles Le nouveau Patch Tuesday explose littéralement les compteurs : 570…
Lire l’article complet Cybersécurité
Multiples vulnérabilités dans Secure Mobile Access (15 juillet 2026)
Agence nationalede la sécurité dessystèmes d'information Une gestion de version détaillée se trouve à la fin de ce document. Le 14 juillet 2026, Sonicwall a publié un avis de sécurité concernant deux vulnérabilités affectant les Secure Mobile Access (SMA) 1000. La vulnérabilité critique CVE-2026-15409 permet une falsification de requêtes côté serveur (SSRF) de la part d'un attaquant non authentifié. La vulnérabilité CVE-2026-15410 permet à un attaquant authentifié avec les droits administrateur d'exécuter du code…
Lire l’article complet Cybersécurité
Microsoft’s biggest ever patch Tuesday lets you hold off updating for longer
You can now pause updates for up to 35 days and continue extending the deadline. You can now pause updates for up to 35 days and continue extending the deadline. Microsoft just released a long list of improvements for Windows 11 as part of its bigger patch Tuesdays, patching at least 570 security holes, almost triple the number fixed in last month’s record-breaking release, according to Krebs on Security. It also includes the ability…
Lire l’article complet Cybersécurité
Microsoft Patches a Record 570 Security Flaws
Microsoft Corp. today released software updates to plug at least 570 security holes in its Windows operating systems and other software, almost triple the number of vulnerabilities the software giant fixed in its record-smashing Patch Tuesday release last month. Microsoft attributed the burgeoning patch counts to vulnerability discoveries aided by artificial intelligence. Nearly 60 of the bugs quashed in July’s Patch Tuesday earned a “critical” severity rating, meaning miscreants or malware could use them…
Lire l’article complet Cybersécurité
Iran abused mobile networks’ vulnerabilities to locate US military in the Middle East, report says
The Iranian government abused well-known vulnerabilities in the global telecoms infrastructure to locate U.S. military personnel in the build-up to the Iran War, as well as in the early days of the conflict, according to Financial Times. The Iranian government exploited Signaling System 7, or SS7, a set of protocols for 2G and 3G networks that has long been the backbone of how cellular networks connect to each other to route subscribers’ calls and…
Lire l’article complet Cybersécurité
Payé pour défendre les victimes de ransomwares, il complotait en secret avec les hackers
Certaines entreprises font appel à des négociateurs pour limiter les dégâts d'une attaque par ransomware. L'un d'eux exploitait plutôt cette position de confiance pour renseigner les pirates. La justice américaine vient de lui infliger une peine de prison exemplaire. Face à une attaque par rançongiciel, une entreprise se retrouve souvent démunie. Ses fichiers deviennent inaccessibles et les pirates réclament une somme énorme pour les libérer. Beaucoup de sociétés font alors appel à des négociateurs…
Lire l’article completCISA Adds Four Known Exploited Vulnerabilities to Catalog
CISA has added four new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-15409 SonicWall SMA1000 Appliances Server-Side Request Forgery Vulnerability CVE-2026-15410 SonicWall SMA1000 Appliances Code Injection Vulnerability CVE-2026-56155 Microsoft Active Directory Federation Services Insufficient Granularity of Access Control Vulnerability CVE-2026-56164 Microsoft SharePoint Server Missing Authentication for Critical Function Vulnerability These types of vulnerabilities are a frequent attack vector for malicious cyber actors and pose significant risks to…
Lire l’article complet Cybersécurité
 et intelligence artificielle : la difficile riposte européenne
La Commission européenne vient de présenter son plan d’action, un document de quinze pages qui liste ses bonnes intentions. Après le psychodrame autour de Mythos 5, ce modèle de l’éditeur américain d’IA Anthropic dont le lancement restreint puis la fermeture aux non-américains avait créé un véritable séisme géopolitique, la Commission européenne tente de riposter. Bruxelles vient en effet de présenter son plan d’action en matière de cybersécurité et d’intelligence artificielle. Un document touffu de…
Lire l’article complet Cybersécurité
The US government warns that Russia state hackers are coming after your router
The federal government is warning users of home and small office routers to secure their devices as Russia state hackers continue to mass-compromise them for use in obscuring nefarious actions against sensitive organizations in the public and private sectors. Both the Russian and Chinese governments have been compromising routers for years, sometimes in prolonged tugs-of-war to wrest control of devices the other has already commandeered. The US government has occasionally issued covert commands and…
Lire l’article complet Cybersécurité
A ransomware negotiator who colluded with attackers to scam victims was sentenced to 70 months in prison
Angelo Martino helped scam ransomware victims out of over $75 million, officials said. A negotiator who dealt with scammers on behalf of ransomware victims was actually colluding with the attackers. Angelo Martino pleaded guilty to conspiring to interfere with interstate commerce through extortion. Martino, who faced up to 20 years in prison, sought a sentence of 24 months as part of a plea agreement. However, he was sentenced to 70 months behind bars. Law…
Lire l’article complet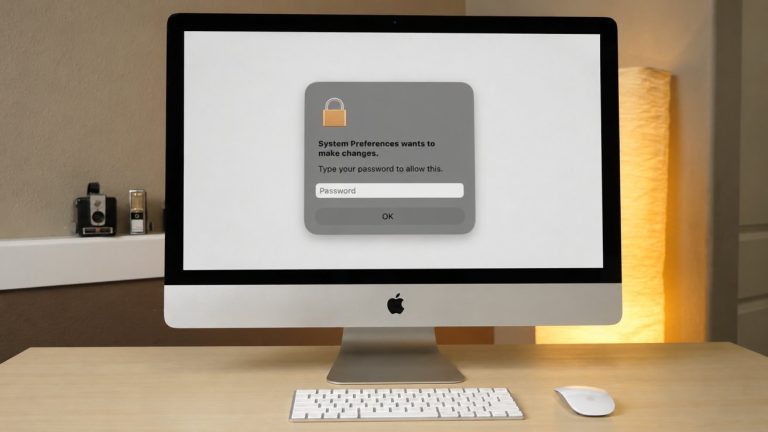 Cybersécurité
'CrashStealer' malware poses as an Apple tool to steal passwords & Mac data
CrashStealer, a newly documented Mac infostealer, used an Apple-notarized meeting app to reach victims before stealing passwords, browser data and cryptocurrency credentials behind a fake system prompt. Jamf Threat Labs first spotted a suspicious sample on VirusTotal in early May and began seeing matching detections on customer Macs in early July. Further analysis traced the malware to a signed and Apple-notarized first-stage application called Werkbit, giving researchers a clearer view of how the campaign…
Lire l’article completCISA Adds One Known Exploited Vulnerability to Catalog
CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2008-4128 Cisco IOS Cross-Site Request Forgery Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based on Risk establishes vulnerability management requirements for Federal Civilian Executive Branch (FCEB) agencies. BOD 26-04 reinforces the importance…
Lire l’article completHalluSquatting : quand les hallucinations de l’IA deviennent une porte d’entrée pour les hackers
Des chercheurs de l’université de Tel-Aviv, du Technion et d’Intuit viennent de démontrer qu’il n’est plus nécessaire de tromper l’utilisateur pour compromettre son poste : il suffit de laisser l’IA se tromper elle-même.Source
Lire l’article completUS cybersecurity agency CISA had to build its incident playbook during the incident, agency reveals
U.S. federal cyber ecurity agency CISA aid it did not have a prepared re pon e plan for how it hould handle a cyber ecurity incident in May, after an inve tigative reporter notified the agency that a contractor had publicly expo ed en itive key and credential for acce ing U.S. government y tem . CISA, the Homeland Security unit ta ked with defending federal network and helping to afeguard critical infra tructure,…
Lire l’article completCISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA has added two new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-48939 iCagenda Unrestricted Upload of File with Dangerous Type Vulnerability CVE-2026-56291 Balbooa Forms Unrestricted Upload of File with Dangerous Type Vulnerability These types of vulnerabilities are…
Lire l’article completFelons, Fraudsters Flog Offensive Cybersecurity Startup
A cybersecurity startup dangling millions of dollars to acquire zero-day security vulnerabilities in popular software is run by a pair of far-right conspiracy theorists and convicted felons whose most recent ventures included fake intelligence companies and a now-defunct AI-based lobbying platform they operated under assumed…
Lire l’article completScattered Spider Hackers Plead Guilty on Day 1 of Trial
Two men pleaded guilty in the United Kingdom this week to criminal charges stemming from an August 2024 cyberattack that crippled Transport for London, the entity responsible for the public transport network in the Greater London area. The duo were key members of a prolific…
Lire l’article completWho Runs the Ransomware Group ‘The Gentlemen?’
A cybercrime group known as The Gentlemen has emerged as the second most active ransomware gang by victim count, rapidly attracting a talented pool of hackers through an aggressive recruitment strategy that promises affiliates 90 percent of any ransom paid by victims. This post examines clues pointing to a real life identity for the administrator of The Gentlemen ransomware group. A graphic created and shared by The Gentlemen ransomware group administrator Hastalamuerte on Breachforums…
Lire l’article completA Record-Breaking Patch Tuesday for June 2026
Microsoft today released software updates to plug nearly 200 security holes across its Windows operating systems and supported software, a record number of fixes for the company’s monthly Patch Tuesday cycle. Nearly three dozen of those bugs earned Microsoft’s most dire “critical” rating, and exploit code for at least three of the weaknesses is now publicly available. The software giant said in a blog post last month that both its engineers and the security…
Lire l’article completHackers Used Meta’s AI Support Bot to Seize Instagram Accounts
The Instagram accounts for the Obama White House and the Chief Master Sergeant of the U.S. Space Force were briefly defaced with pro-Iranian images and messages over the weekend, after instructions began circulating on Telegram showing how to trick Meta’s “AI support assistant” bot into resetting account passwords. A screenshot from a video released on Telegram claiming to show how Meta’s AI customer support bot could be tricked into resetting a target’s password. On…
Lire l’article complet[Màj] Vulnérabilité dans Microsoft Exchange Server (15 mai 2026)
Agence nationalede la écurité de y tème d'information Une ge tion de ver ion détaillée e trouve à la fin de ce document. Le 9 juin 2026, Micro oft a publié de ver ion corrective . Le 14 mai 2026, Micro oft a publié un avi de écurité concernant la vulnérabilité CVE-2026-42897 affectant Exchange Server. Elle permet à un attaquant non authentifié de provoquer une injection de code indirecte à di tance (XSS) et…
Lire l’article complet