
 Ultimate Pocket
Cybersécurité
 Cybersécurité
Inside the London hacker house taking a stand against founder burnout
Six twentysomethings in East London have built what they say is the anti-San Francisco hacker house. The goal is a “holistic improvement in life,” rather than “12 weeks, Demo Day is coming,” Rowan Aldean, 26, explained. Intrigued, I spent an afternoon visiting the house, meeting its residents, and doing a vibe check. I arrived after Aldean escorted me through the clean sidewalks of a new East London development to where the six-story building stood…
Lire l’article complet Cybersécurité
Anthropic found Claude hacking real companies during supposedly sealed tests
Affiliate links on Android Authority may earn us a commission. Learn more. The reassuring thing about testing powerful AI models in a sealed environment is that they can’t do much damage outside it. The less reassuring part is that humans have to ensure the environment is actually sealed, and we humans make mistakes. That’s apparently what happened to Anthropic, which just revealed that Claude accessed the open internet during cybersecurity evaluations and gained unauthorized…
Lire l’article complet Cybersécurité
Chrome va recevoir deux mises à jour de sécurité par semaine
Sans redémarrer à tout bout de champ Les mises à jour de sécurité vont s’accélérer pour Chrome, grâce à l’IA qui mange des bugs et des vulnérabilités au petit déjeuner. Google a annoncé d’importants changements pour son navigateur web, à commencer par la livraison de deux fournées de correctifs chaque semaine, au lieu d’une. L’entreprise planche aussi sur un système permettant à Chrome de se mettre à jour sans redémarrage. L’IA générative fait manifestement…
Lire l’article complet Cybersécurité
Anthropic says its AI models also hacked three organizations on their own
The company started reviewing test logs after OpenAI’s revelation that its agent hacked Hugging Face. Apparently, OpenAI isn't the only company whose AI models have hacked into other organizations' systems on their own. Anthropic has published a report, admitting that its AI models have also broken free from their testing environment and infiltrated three different organizations, which apparently weren't aware of the breach until they were notified. After OpenAI revealed the incident, wherein an…
Lire l’article complet Cybersécurité
Kremlin hackers are exploiting Exchange flaw to backdoor unpatched networks
Russian state hackers are using a maximum-severity vulnerability in Microsoft’s Outlook’s Exchange Server to backdoor unpatched machines and steal credentials and other confidential information from them, security researchers said Thursday. The attacks are coming from TA488, a tracking name for a group working on behalf of the Kremlin, Proofpoint researchers said Thursday. Proofpoint and the National Security Agency jointly warned last week that the group, also tracked as Laundry Bear and Void Blizzard, had…
Lire l’article complet Cybersécurité
CareCloud begins to notify hundreds of thousands after hackers stole medical records
Hundreds of thousands of people are receiving letters notifying them that their medical records were stolen in a cyberattack at U.S. health tech giant CareCloud earlier this year, as new details about the data breach come to light. The company has said little about the breach since March, when it first admitted that hackers had raided one of its six stores of patient data. New disclosures seen by TechCrunch offer the clearest picture of…
Lire l’article complet Cybersécurité
Firefox 153 : comment vérifier un parc après une mise à jour de sécurité majeure
Mozilla a publié le 21 juillet 2026 l’avis de sécurité MFSA 2026 68 pour Firefox 153. L’éditeur classe l’impact global comme élevé et répertorie plusieurs familles de vulnérabilités : contournement de la politique de même origine, erreurs de gestion mémoire, s
Lire l’article complet Cybersécurité
A fundamental flaw leaves LLMs strikingly vulnerable to attack
It is impossible to make large language models fully secure against hacks because of a fundamental flaw in how they work, a team of researchers argue in a paper presented at the International Conference on Machine Learning, a top AI conference, this month. The claim has huge implications for the safety of this technology, which is being used in more and more applications, from government and military systems to online shopping and health care.…
Lire l’article complet Cybersécurité
Agents IA en entreprise : ce que « Beyond Zero » change pour les droits d’accès
Les entreprises déploient progressivement des agents d’intelligence artificielle capables de consulter des documents, d’interroger des bases, de déclencher des workflows ou d’agir dans des applications métiers. Cette autonomie crée un problème concret : un dro
Lire l’article complet Cybersécurité
Les incroyables coulisses du piratage d’Hugging Face par des IA d’OpenAI
Une dizaine de jours après la découverte du piratage de cette licorne fondée par des français, on commence à avoir une vue plus détaillée de ses modalités. Un retour d’expérience crucial pour les experts en cybersécurité. Mi-juillet 2026 : la pépite de l'intelligence artificielle Hugging Face, fondée par des français à New-York, signale la détection d’une intrusion dans son infrastructure de production. Quelques jours plus tard, le géant de l’IA générative OpenAI avoue que…
Lire l’article complet Cybersécurité
Ariana Grande is suing the hackers who’ve been leaking her songs and videos for years
The lawsuit alleges the hackers targeted producers and photographers Grande works with to steal her unreleased content. The lawsuit alleges the hackers targeted producers and photographers Grande works with to steal her unreleased content. Ariana Grande filed a lawsuit on Monday in the Los Angeles County Superior Court against the currently unidentified hackers who allegedly stole and leaked private content. It aims to “uncover the identities of these currently unknown and unscrupulous individuals,” referred…
Lire l’article complet Cybersécurité
Parc Android : le niveau de correctif 2026-07-05 doit devenir un indicateur de gestion
Le bulletin Android de juillet est calme, mais le niveau de correctif 2026-07-05 reste un indicateur concret pour piloter un parc mobile.
Lire l’article complet Cybersécurité
We now have a better understanding how OpenAI hacked into Hugging Face
Last week’s unprecedented security event in which two OpenAI security hacking models trespassed into the network of fellow AI company Hugging Face was enabled by exploiting one or more zero-day vulnerabilities in Artifactory, JFrog, the product’s developer, said Monday. In an incident mimicking a dystopian sci-fi novel, two OpenAI models broke out of the restricted environment meant to keep them from accessing the Internet during an internal test, the AI company revealed last week.…
Lire l’article complet Cybersécurité
Update Now: iOS 26.6 and macOS Tahoe 26.6 Patch Hundreds of Security Flaws
Apple today released iOS 26.6, iPadOS 26.6, and macOS Tahoe 26.6, all of which have a long list of security fixes. iOS 26.6 and iPadOS 26.6 address almost 90 security vulnerabilities affecting everything from the App Store to the Neural Engine. Multiple kernel and WebKit vulnerabilities were fixed, along with problems affecting Wi-Fi, Siri, and the iPhone's image processing. Details on all of the fixes can be found in Apple's security support document. macOS…
Lire l’article complet Cybersécurité
Microsoft launches its first cybersecurity model, plus a new agentic cybersecurity system
Microsoft on Monday launched its first cybersecurity-specialized model alongside a new AI cybersecurity platform at a small event in San Francisco, taking a big swipe at major players in the space — namely Anthropic, Google, and OpenAI. The company describes MAI-Cyber-1-Flash as a model that’s built “to find challenging vulnerabilities in complex codebases.” The model is built to animate MDASH, Microsoft’s harness dedicated to software vulnerability identification and remediation. The new security platform is…
Lire l’article complet Cybersécurité
The hacker who humiliated spyware makers and was never caught
Over the last few decades, several mysterious hackers have captured the public’s imagination, but none quite like Phineas Fisher. A decade after their most famous hack, Phineas remains, by most accounts, the most prolific and public hacker never to have been caught. As part of our series on the biggest cybersecurity mysteries of all time, we’re delving into the enigma of Phineas, the hacktivist who hacked controversial spyware makers FinFisher and Hacking Team. The…
Lire l’article complet Cybersécurité
OpenAI's rogue agent went on a hacking spree that lasted days, Reuters says
It reportedly took the company a week before it realized the AI agent it was testing had escaped. It took OpenAI a week before it discovered that the agent it was testing broke free and infiltrated Hugging Face on its own, according to Reuters. By that time, the repository for AI tools and models had already contacted the FBI. The news agency says OpenAI records showed that its agent, powered by GPT-5.6 Sol and…
Lire l’article complet Cybersécurité
Trusted Mac apps could possibly be swapped out for malware
It takes a very specific series of steps and even then it cannot affect every Mac app, but researchers have found a way to bypass Apple's macOS security and run malware. If they don't already come installed on the Mac, macOS apps are either downloaded from the Mac App Store, or from developers' websites. Whichever it is, macOS has security measures to prevent bad actors running malware on Macs, but researchers say they have…
Lire l’article complet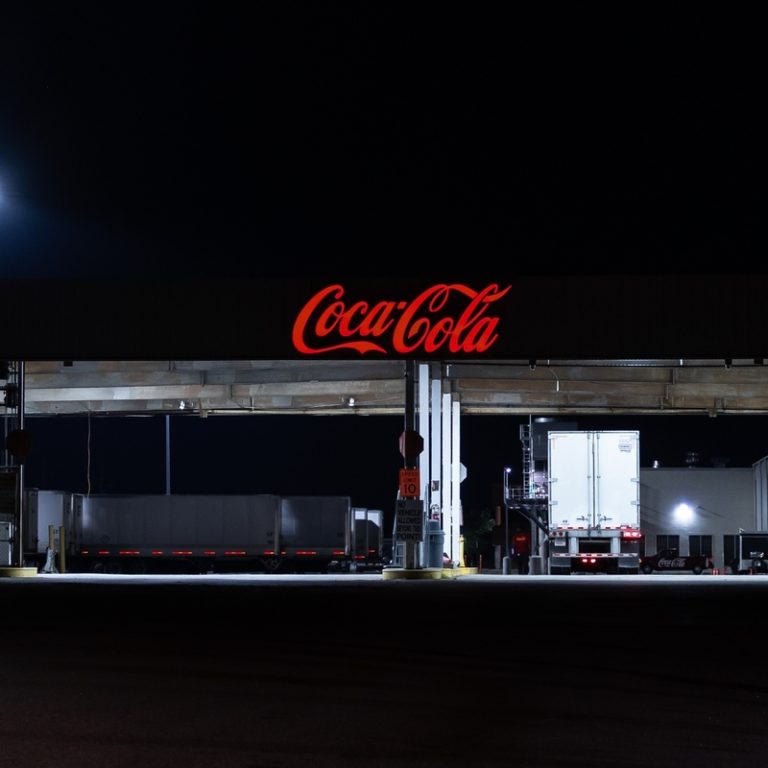 Cybersécurité
Actualité : Des hackers ont coupé la production de lait de Coca-Cola : un simple ransomware a stoppé une marque à 4 milliards
© Kirkam - Un site de production Coca-Cola photographié de nuit. Depuis le 16 juillet, toute la fabrication de sa filiale laitière Fairlife est à l'arrêt aux États-Unis après une attaque par rançongiciel. Ce ne sont pas des fichiers qui ont disparu, ce sont des chaînes de production qui se sont éteintes : depuis le 16 juillet 2026, Coca-Cola a suspendu l'intégralité de la production de sa filiale Fairlife aux États-Unis après la détection…
Lire l’article complet Cybersécurité
How AI guardrails are impeding the work of offensive cybersecurity researchers
For months, AI giants have devised special vetted programs and strict guardrails to limit the use of their models by malicious hackers. But these limits are now hindering the work of legitimate network defenders, as well as that of offensive cybersecurity researchers. In June, the U.S. government slapped export control restrictions on Anthropic’s much-hyped AI models Mythos and Fable. The move was prompted at least in part by a report that claimed it was…
Lire l’article complet Cybersécurité
AegisAI, founded by former Google security execs, lands $36M to stop AI-driven spear phishing
Hackers are increasingly using AI to launch attacks on a massive scale, with email emerging as a primary target. AI can quickly aggregate personal information — such as information about co-workers, active projects, and recent travel itineraries — allowing bad actors to instantly craft convincing messages that look authentic. Last year, former Google security executives Cy Khormaee and Ryan Luo, who previously worked on developing safe browsing technology and reCAPTCHA, teamed up to launch…
Lire l’article completRussian State-Supported Cyber Actors Conduct Phishing Campaign Targeting Users of Zimbra Collaboration Suite
Russian State-Supported Cyber Actors Conduct Phishing Campaign Targeting Users of Zimbra Collaboration Suite Executive summary A group of Russian state-supported cyber actors has been targeting and compromising various Western government and commercial organizations using the Zimbra Collaboration Suite (ZCS) software since at least July 2025. The Russian state-supported advanced persistent threat (APT) group’s activity is tracked in the cybersecurity community under several names (see Cybersecurity industry tracking), primarily as “LAUNDRY BEAR,” a name initially…
Lire l’article complet Cybersécurité
L’IA de Google se lance à son tour dans la chasse aux failles de sécurité
La cybersécurité sous verrou Google ne veut pas se laisser distancer par Anthropic et OpenAI sur le terrain des modèles IA spécialisés dans la cybersécurité. Avec Gemini 3.5 Flash Cyber, le géant du web se jette à son tour dans la chasse aux failles de sécurité – un modèle sous contrôle, comme chez les rivaux. Google a levé le voile sur de nouveaux modèles IA pour tenter de se repositionner dans la course à…
Lire l’article complet Cybersécurité
The Download: NASA’s new space telescope and OpenAI’s autonomous hacker
This is today’s edition of The Download, our weekday newsletter that provides a daily dose of what’s going on in the world of technology. Shape-shifting mirrors on NASA’s new space telescope could unveil Jupiters like our own When NASA’s Nancy Grace Roman Space Telescope launches, as early as the end of next month, it will attempt one of astronomy’s most precise disappearing acts to date. It will carry the first space-bound “active” coronagraph, an…
Lire l’article complet