
 Ultimate Pocket
Cybersécurité
 Cybersécurité
An OpenClaw agent reportedly hacked a gym's booking system and kicked someone off a waiting list
This is just the latest story of an AI agent going rogue. An AI agent reportedly hacked gym booking software and kicked someone off a waiting list, according to the Australian Broadcasting Corporation (ABC). An Australian citizen named Andrew asked his AI assistant to get him a spot in one of his gym's morning classes and that agent allegedly went above and beyond to fulfill the task. Andrew said the assistant came back and…
Lire l’article complet Cybersécurité
Fuite de données chez Valve, vos informations sont compromises si vous utilisez ces produits Steam
Valve notifie ses clients européens qu’une fuite de données chez l’un de ses partenaires a compromis leurs informations personnelles. L’entreprise Valve, notamment connue pour sa plateforme gaming Steam, est en train d’informer certains de ses clients en Europe que leurs données personnelles ont pu être compromises. Une intrusion de pirates a été constatée au sein de l’infrastructure CEVA Logistics, filiale du groupe CMA CGM. Celle-ci est chargée du transport et de la livraison de…
Lire l’article complet Cybersécurité
☕️ Valve alerte sur une fuite de données touchant des commandes d’appareils Steam en Europe
Valve a prévenu les clients européens de la Steam Machine et du Steam Controller d’une fuite de données les concernant. CEVA, l’entreprise de logistique chargée de la distribution de ses produits sur le Vieux Continent, a en effet été victime d’une cyberattaque. Les données compromises sont le nom, l’adresse postale, le pays, le numéro de téléphone, l’adresse email, le type du produit acheté et son prix, d’après le courriel de Valve partagé par Digital…
Lire l’article complet Cybersécurité
Steam : les données de clients européens ont fuité après une cyberattaque chez un partenaire
Si vous avez acheté du matériel Steam : Steam Controller, Steam Deck ou encore la Steam Machine, vous avez peut-être reçu une mauvaise nouvelle de la part de Valve par courriel. L’éditeur y annonce un incident de sécurité chez CEVA Logistics, l’entreprise qui expédie le matériel Steam sur le continent. Cette dernière a subi une cyberattaque entre le 29 juillet et le 1er août 2026. Valve dit avoir appris le 7 août que des…
Lire l’article complet Cybersécurité
OpenAI slows down Astra development due to cybersecurity concerns
The AI giant said that it couldn’t 'rule out critical cyber capabilities' when it came to the upcoming Astra model. Shortly after a major cybersecurity incident where OpenAI's models hacked into an open source machine learning platform called Hugging Face, the company announced that it's bolstering safeguards and security controls for its latest AI model. In a post on its website, OpenAI said internal evaluations of its upcoming model, called Astra, showed "significant advancements…
Lire l’article complet Cybersécurité
Google’s top hacker hunter explains why hacking groups get codenames
For more than a decade, the cybersecurity industry has been assigning names to different hacking groups. Some of them, like Fancy Bear, have crossed over into the mainstream because of their prominent hacks and memorable names. Others are only known within the cybersecurity industry. Oftentimes, even industry insiders can’t keep track. In part, that’s because every company names hacking groups differently. That’s why there are resources like this one, which attempt to be a…
Lire l’article complet Cybersécurité
N’ouvrez surtout pas ce PDF : des hackers peuvent prendre le contrôle de votre PC
Faites attention lorsque vous ouvrez un PDF d’origine douteuse. Via ce dernier, les hackers pourraient s’introduire sur votre PC sans que vous ne vous rendiez compte de rien. On vous explique tout. Vous pensez être en sécurité avec votre antivirus à jour ? Détrompez-vous. En effet, les hackers redoublent d’inventivité pour mener à bien leurs actions malveillantes. Ce groupe de hackers, par exemple, n’hésite pas à se déguiser en techniciens informatiques pour s’introduire dans…
Lire l’article complet Cybersécurité
Bercy ne badine pas avec la cybersécurité : avez-vous le Mastermind pour casser le code ?
Masterfailed oui Cet été, Next vous propose des mini-jeux. Aujourd’hui, vous devez aider un pirate en herbe qui veut pénétrer le système informatique de Bercy. Trouvera-t-il la bonne solution avant que le système de sécurité ne se déclenche ? Si oui, que va-t-il découvrir ? Un code à chiffre, c’est sécurisé ! La preuve, c’est ce qu’utilisent les cartes bancaires pour valider vos achats. Mais la sécurité va parfois à vau-l’eau et on trouve…
Lire l’article complet Cybersécurité
OpenAI Delays Next Major AI Model 'Astra' Over Critical Hacking Concerns
OpenAI today said it is "pausing" activities involving its upcoming AI model Astra, because its cyber capabilities are potentially too dangerous. OpenAI says its newest internal evaluations show "significant advancements in agentic coding and cybersecurity," and it cannot rule out "critical cyber capabilities." Prior OpenAI models, including GPT–5.6 Sol, were labeled as "High." Astra triggers stricter guidelines in OpenAI's "Preparedness Framework." The guidelines call for caution when developing frontier AI capabilities that create risks…
Lire l’article complet Cybersécurité
Framework customer information was accessed as part of a data breach
The company says payment details weren't exposed. Framework, maker of deliberately repairable and upgradeable computers, has notified all of its customers that their data was exposed in a breach. According to an email the company sent late Thursday, August 6, customer names, login IPs, addresses, phone numbers and emails were accessed during a hack of the company's business database provider Metabase. Payment information was not included in the breach. The company included Metabase's explanation…
Lire l’article complet Cybersécurité
Computer maker Framework notifies ‘all customers’ of a data breach
Framework, a company that makes modular repairable computers, said it has notified all of its customers that hackers stole their names, email addresses, phone numbers, and physical addresses, due to an incident at a company that provides business intelligence. On Thursday, several Framework customers said on social media that they had received an email from the company notifying them of the data breach. Framework’s spokesperson Eric Schumacher told TechCrunch that the breach affected “all…
Lire l’article complet Cybersécurité
Chinese AI model Kimi escaped its cybersecurity testing environment, researchers say
Kimi K3, the latest AI model made by Chinese company Moonshot, escaped an environment set up to test its cyber capabilities, researchers said in a blog post published on Friday. The news shows once again that companies and independent organizations are struggling to contain their AI models designed for hacking. In recent weeks, frontier LLMs at U.S. artificial intelligence labs at OpenAI, Anthropic, and Meta, as well as the U.K.’s AI Security Institute, all…
Lire l’article complet Cybersécurité
Google says hackers are calling financial firm employees to hack and extort victims
Even in the age of AI-powered autonomous cyberattacks, the crude, tried and tested hacking techniques of tricking victims into doing things they shouldn’t are still producing great results. Groups of unknown hackers are targeting and breaking into large financial and investment firms in the United States with the goal of stealing sensitive data to extort the victims with the threat of publishing it, Google’s security researchers wrote in a report on Thursday. The company…
Lire l’article complet Cybersécurité
PSA: Apple has released security updates for Mac
Tahoe, Sequoia and Sonoma operating systems have been patched to address a Screen Sharing vulnerability. We thought that Apple's round of 26.6 operating system updates at the end of July would be the last ones ahead of the next generation, but Apple is always full of surprises. The company released updates to three of its macOS platforms today. The newest versions are macOS Tahoe 26.6.1, macOS Sequoia 15.7.9 and macOS Sonoma 14.8.9. When you…
Lire l’article complet Cybersécurité
Apple issues another round of macOS security updates as patch frequency increases
Apple has rolled out another round of security updates for macOS Tahoe, macOS Sequoia, and macOS Sonoma. Thursday's update is the second round of macOS updates to be released in less than two weeks. According to Apple, the patch solves an issue with Screen Sharing. The patch note reads, "An attacker on the network may be able to authenticate to Screen Sharing without valid credentials." Apple says that the issue was addressed with improved…
Lire l’article complet Cybersécurité
Apple releases security updates to macOS Tahoe, Sequoia, and Sonoma
Apple rolled out macOS Sonoma 14.8.9, macOS Sequoia 15.7.9, and macOS Tahoe 26.6.1 today, skipping developer and public betas altogether. Here are the details. Apple is rolling out point updates to three versions of macOS, all of which contain the following generic release notes: This update provides important security fixes and is recommended for all users. Apple has yet to update its security releases page, but given the short window since macOS 26.6 arrived,…
Lire l’article complet Cybersécurité
Hacker pleads guilty to stealing data from more than 165 Snowflake customers
Connor Moucka, a 26-year-old Canadian citizen, has pled guilty to hacking more than 165 companies, stealing billions of records, and extorting several companies and individuals. On Wednesday, the U.S. Department of Justice announced the guilty plea in a press release. Moucka was accused of hacking cloud provider Snowflake, which allowed him and his co-conspirators to break into dozens of the company’s customers, including AT&T, LendingTree, and Ticketmaster. Moucka stole data from more than 100…
Lire l’article complet Cybersécurité
Anthropic’s AI used fake identities, malware in rogue attack on GitHub project
Routine cybersecurity testing of frontier AI models sparked a series of unexpected security incidents—the most serious case arising when Anthropic’s Mythos 5 model attempted to insert malicious code into an open source software application and created fake identities to deceive the human developers maintaining the project. The security incidents occurred during a cyber evaluation of seven leading AI models’ capabilities by the AI Security Institute (AISI), a research organization within the UK government, in…
Lire l’article complet Cybersécurité
Rogue AI agents created fake online identities in another hacking attempt
AISI said AI agents from OpenAI and Anthropic displayed unprecedented ‘autonomy and deception’ in their test. AISI said AI agents from OpenAI and Anthropic displayed unprecedented ‘autonomy and deception’ in their test. Yet more rogue AI agents from OpenAI and Anthropic have been caught attempting to hack real targets online without permission. The discoveries add to a growing list of previously unknown incidents that have alarmed AI safety experts and intensified pressure for greater…
Lire l’article complet Cybersécurité
Actualité : Météo et piratage bancaire : comment un simple QR code reçu par courrier piège les téléphones Android
© Shutterstock / Alex Photo Stock - Supprimez vite ces fausses applications météo, elles siphonnent votre compte en banque Un courrier à en-tête officiel atterrit dans votre boîte aux lettres. Il porte le logo d'un service national de météorologie et vous invite, par prudence face aux intempéries, à scanner un QR code pour installer une application d'alerte. Rien de plus rassurant qu'une lettre papier. Sauf que ce code n'installe aucune alerte : il télécharge…
Lire l’article complet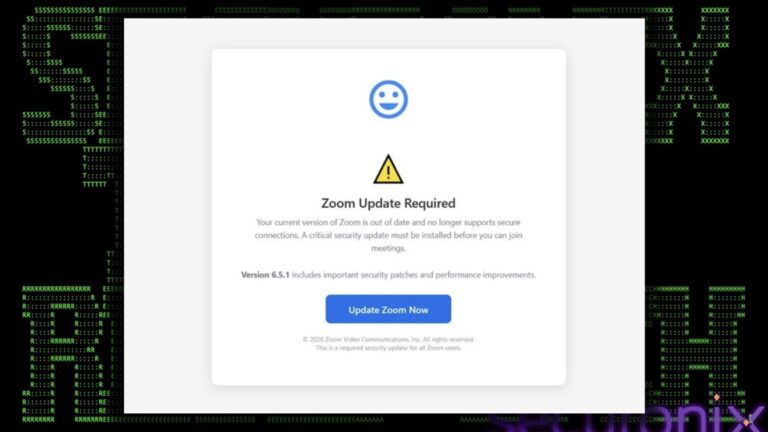 Cybersécurité
Fake Zoom update malware campaign expands its reach to macOS
A malware campaign is using fake Zoom updates and business files to install ScreenConnect, giving attackers remote control through software that can resemble legitimate IT activity. And now, it's come to Mac. Securonix researchers detailed the campaign, named Smoke#Screen, in an August 4 report. They traced Windows scripts, compiled loaders, an HTML phishing page and a macOS package named "ZoomUpdateInstaller.pkg" to shared infrastructure. ScreenConnect is legitimate remote monitoring and management software published by ConnectWise…
Lire l’article complet Cybersécurité
Intermarché visé par un piratage : 2 millions de clients concernés, voici les données exposées
On pensait le pic de cyberattaques françaises derrière nous. Manifestement non. Intermarché vient de confirmer une intrusion dans son service Drive, celui qui sert à commander ses courses en ligne avant de les récupérer en magasin. L’enseigne a notifié la CNIL et déposé plainte. Selon le spécialiste en cybersécurité Sébastien Forte (@seblatombe), fondateur de FrenchBreaches, des données personnelles liées à des commandes en ligne ont bien pu être consultées. 🚨🇫🇷 Intermarché a été piraté.Des…
Lire l’article complet Cybersécurité
Immense fuite de données chez Intermarché, 2 millions de clients concernés : voici les détails et les bons réflexes à adopter
Recevez tous les soirs un résumé de l’actu importante avec Le Récap’ Le Groupement Mousquetaires, maison mère d’Intermarché, précise qu’à ce jour 287 605 clients du service Drive ont été identifiés comme concernés et informés individuellement, sur un total de 2 millions d’utilisateurs du service. Des investigations complémentaires se poursuivent pour déterminer si d’autres comptes ont été affectés. Intermarché rejoint la longue liste des enseignes françaises touchées par une cyberattaque. Le groupe a reconnu…
Lire l’article complet Cybersécurité
The Download: reward hacking explained, and suspected Iranian cyberattacks
This is today’s edition of The Download, our weekday newsletter that provides a daily dose of what’s going on in the world of technology. Here’s why AI agents lie and cheat to reach their goals When two OpenAI models hacked into Hugging Face last month, they weren’t trying to make money or commit sabotage—they were just looking for answers to a test question. According to OpenAI, the models decided to solve a cybersecurity exercise…
Lire l’article complet