
 Ultimate Pocket
Cybersécurité
 Cybersécurité
Les hackers russes reviennent aux basiques du piratage et Microsoft rebaptise leur méthode
Recevez tous les soirs un résumé de l’actu importante avec Le Récap’ Depuis plusieurs mois, ClickFix s’est imposé comme l’une des techniques préférées des hackers. Le principe est simple et un peu vicieux, puisque la victime installe elle-même le malware. Un faux message d’erreur ou une fausse vérification CAPTCHA lui demande de copier une commande, de l’insérer dans la fenêtre « Exécuter » de Windows et de valider, sans se douter qu’elle vient de…
Lire l’article complet Cybersécurité
Dutch police arrest ShinyHunters hacker accused of planning two murders
The FBI and Dutch law enforcement say they have arrested a member of the ShinyHunters hacking group, which the agencies say are responsible for hacks on over 140 organizations around the world. The hackers also claimed responsibility for a breach of the FBI’s own systems earlier this month. Brett Leatherman, the FBI’s cyber division lead, said in a video message on Tuesday that Dutch authorities had arrested one of the “alleged leaders of ShinyHunters.”…
Lire l’article complet Cybersécurité
Des mots de passe volés ont suffi, et personne n’a rien vu : l’ANSSI dissèque le piratage de la DGFiP
Recevez tous les soirs un résumé de l’actu importante avec Le Récap’ Plusieurs signaux d’alerte existaient, mais ils n’ont pas été corrigés. En août 2026, le groupe Zerobytes avait revendiqué le vol de données issues de services de la Direction générale des Finances publiques (DGFiP). Un premier jeu provenait de l’outil de contact avec les usagers, E-Contact, un second concernait des données cadastrales, obtenues via un accès utilisé par un cabinet de géomètres-experts. La…
Lire l’article complet Cybersécurité
iOS 26.7.1 Fixes Vulnerability Used in Targeted Attacks
iOS 26.7.1, iPadOS 26.7.1, macOS Tahoe 26.7.1, and macOS Sequoia 15.8.1 address a major vulnerability that Apple believes was used against a small number of people. Apple's security support pages say there was a CoreGraphics out-of-bounds write issue that could be exploited with a maliciously crafted file, allowing for arbitrary code execution. It has been fixed with improved bounds checking. Apple says the flaw was exploited in an "extremely sophisticated attack" on targeted individuals…
Lire l’article complet Cybersécurité
AI is supercharging hacking, and your local hospitals and banks aren’t ready
New models are helping Big Tech shore up its cyber defenses. What about everyone else? New models are helping Big Tech shore up its cyber defenses. What about everyone else? In March, Janice Malone began getting calls about suspicious activity from her nonprofit organization, Vivian’s Door. Vivian’s Door, headquartered in Alabama, typically provided training, resources, and community to underserved and minority-owned businesses. The work sometimes put it in close contact with these companies’ financial…
Lire l’article complet Cybersécurité
Dutch Police Arrest ‘Reformed’ Hacker in Shiny Hunters Investigation
Authorities in the Netherlands have arrested a 23-year-old convicted cybercriminal on suspicion of aiding in data thefts and extortions by the prolific hacker group ShinyHunters. In the days immediately following the suspect’s arrest, remaining ShinyHunters members dramatically escalated their attacks, stealing highly sensitive data from the FBI and extorting the Russian ransomware group Cl0p. According to three sources familiar with the matter, the Dutch man arrested by authorities this month is Pepijn van der…
Lire l’article completMultiples vulnérabilités dans Citrix NetScaler ADC et Gateway (28 septembre 2026)
Objet : Multiples vulnérabilités dans Citrix NetScaler ADC et Gateway Une gestion de version détaillée se trouve à la fin de ce document. [Mise à jour du 05 octobre 2026] Le 4 octobre 2026, Citrix a publié un avis concernant une nouvelle vulnérabilité (CVE-2026-88779) permettant un déni de service à distance. La CISA indique que cette vulnérabilité est activement exploitée. [Mise à jour du 30 septembre 2026] Dans un billet de blogue du 29…
Lire l’article completMultiples vulnérabilités dans Citrix NetScaler ADC et Gateway (28 septembre 2026)
Agence nationalede la sécurité dessystèmes d'information Une gestion de version détaillée se trouve à la fin de ce document. Le 27 septembre 2026, Citrix a publié un avis de sécurité concernant plusieurs vulnérabilités qui affectent NetScaler ADC et Gateway. Parmi celles-ci, les vulnérabilités CVE-2026-88771 et CVE-2026-88772 permettent une exécution de code arbitraire à distance par un attaquant non authentifié. Ces vulnérabilités sont activement exploitées et les exploitations ont commencé avant la disponibilité des correctifs.…
Lire l’article complet Cybersécurité
, IA et résilience : comment des livres peuvent devenir des outils de protection pour les professionnels et les particuliers
Dans un monde de plus en plus connecté, la cybersécurité et l’intelligence artificielle sont des sujets techniques qui transcendent les frontières. Les livres, souvent perçus comme des supports d’information, peuvent devenir des outils concrets pour mieux comprendre, anticiper et résister aux menaces numériques. Ce texte explore comment l’expertise professionnelle, l’actualité technologique et la culture numérique se croisent pour offrir des solutions tangibles. Comprendre les bases de la cybersécurité : une première étape essentielle La…
Lire l’article complet Cybersécurité
Piratage par IA : un agent d’OpenAI a accédé sans autorisation à un site du gouvernement australien
OpenAI a informé les autorités australiennes plusieurs mois après qu’un agent d’IA a accédé sans autorisation au site de Medicare lors d’un test interne. L’entreprise affirme qu’aucune donnée personnelle de patients n’a été consultée, mais Canberra réclame des explications sur l’incident. Un agent d’intelligence artificielle développé par OpenAI a accédé sans autorisation à un site gouvernemental australien dans le cadre d’une évaluation interne. L’incident, survenu le 18 juin, concerne le site de Medicare, le…
Lire l’article complet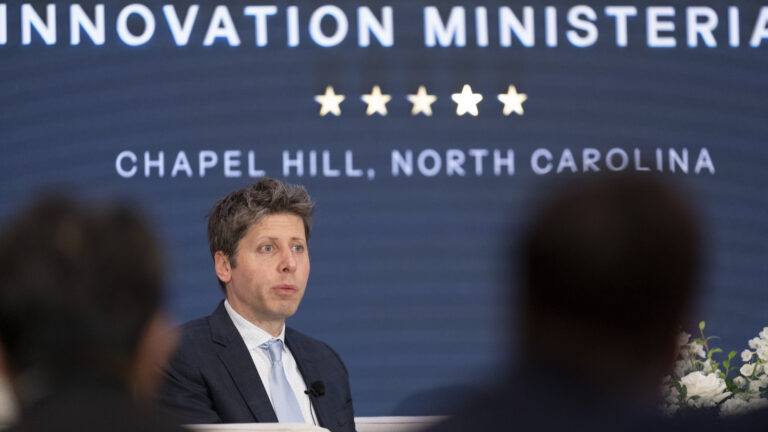 Cybersécurité
OpenAI's agent hacked into an Australian government website
Australia’s prime minister said it doesn’t seem like any personal health information was compromised. An OpenAI agent hacked into the public website of the Australian government's Medicare public health insurance system in June, Australian Prime Minister Anthony Albanese has revealed. Albanese said he spoke with Sam Altman, the company's CEO, to express the country's "extreme concern" about the incident. He also criticized the company for taking too long to notify Australian authorities. According to…
Lire l’article complet Cybersécurité
ShinyHunters hackers claim to have 2-3TB of sensitive information about FBI employees
Financial extortion doesn’t seem to be the group’s goal this time. Hacking group ShinyHunters has allegedly stolen extensive amounts of sensitive information from the US Federal Bureau of Investigation that includes details about its employees and job applicants. Reuters reports that it has seen a sample of the data obtained by the attack on the agency, and 404 Media also said it received confirmation of the action from a representative of ShinyHunters. The hackers…
Lire l’article complet Cybersécurité
The old cybersecurity model is breaking
Disrupt 2026: OpenAI, Anthropic, Replit, and more take over 6 industry stages. 25% off tickets now Disrupt ticket savings of up to $200 + 50% off a second ends Sept 25, 11:59 p.m. PT. REGISTER HERE. As concern over AI safety and rogue agents continue to make headlines, it’s no surprise that cybersecurity stocks are rising, or that investors are pouring massive amounts of capital into startups trying to build the next generation of…
Lire l’article complet Cybersécurité
 et IA : quand l’expertise devient un guide pour agir
La cybersécurité n’est plus une préoccupation réservée aux experts en informatique ou aux grandes entreprises. À l’ère où nos données personnelles, professionnelles et même notre identité numérique circulent en permanence sur des réseaux interconnectés, la menace est omniprésente : ransomwares ciblant les hôpitaux, phishing automatisé par IA, deepfakes manipulant l’opinion publique, ou encore attaques exploitant les failles des objets connectés. Pourtant, ces risques ne se traduisent pas seulement en chiffres alarmants dans les rapports…
Lire l’article complet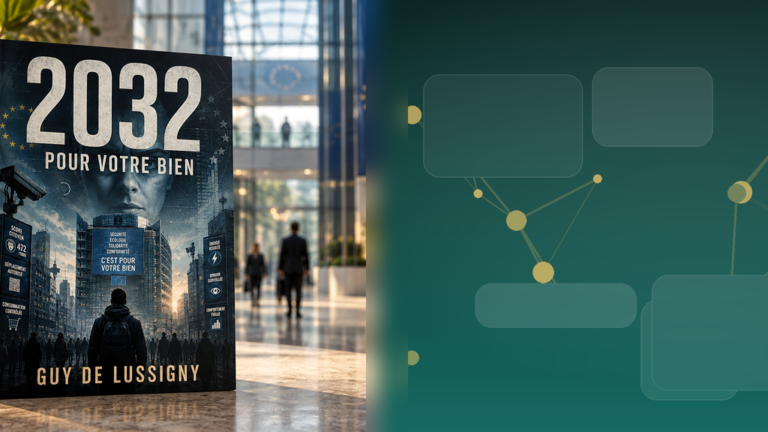 Cybersécurité
Cybersecurite, IA et resilience : comment des livres deviennent des outils de connaissance et de protection
Dans un monde de plus en plus connecté, la cybersécurité et l’intelligence artificielle sont des sujets qui transcendent les frontières techniques. Les livres sur ces thèmes ne sont plus seulement des ouvrages d’expertise, mais des outils concrets pour comprendre, anticiper et protéger. Découvrez comment ces textes deviennent des ressources essentielles pour les professionnels et les particuliers. Comprendre la cybersécurité : les fondamentaux et les enjeux La cybersécurité est aujourd’hui un enjeu central pour tous,…
Lire l’article complet Cybersécurité
Hacking group ShinyHunters claims it breached the FBI, stole agents’ and applicants’ data
ShinyHunters, a prolific cybercriminal group known for large-scale data theft and extortion, says it has breached the FBI and stolen data on thousands of agents and applicants. The hackers made the claim on their dark web leak site, which TechCrunch reviewed, saying they had stolen “sensitive data on almost all FBI agents and individuals who filed an application with the FBI for a job.” 404 Media first reported on the breach after receiving a…
Lire l’article complet Cybersécurité
Google confirms Gemini models hacked three companies in May 2026
It has become increasingly common for AI firms to announce that their latest and most capable models engaged in unauthorized real-world hacking. Google, which has been slow to release frontier Gemini models in recent months, has been absent from the "rogue AI" conversation until now. Following a Wall Street Journal report, Google has confirmed that Gemini models hacked three companies during a May 2026 test, but the nature of the intrusion isn't as troubling…
Lire l’article complet Cybersécurité
Autopsie d’un kit de phishing et de son camouflage
O.D.I.L… ? LIDO, c'est peut-être une danseuse ! Parfois il suffit de peu : un lien et deux trois clics plus tard, voilà que votre boîte email est compromise. Comment fonctionnent les kits de phishing livrés clés en main par certains groupes de pirates ? Nous en avons récupéré et analysé un, conçu pour attaquer des comptes Outlook protégés par une double authentification. Il y a quelques mois, Hexastrike dévoilait une nouvelle attaque baptisée…
Lire l’article complet Cybersécurité
Humans, not rogue AI, are still the biggest cybersecurity risk to energy systems
Before recent high-profile hacks raised the specter of AI possibly “killing all humans,” our energy systems were already disturbingly vulnerable to cyberattack — and the risk is growing. “We were always prey. We were just kind of surviving at the appetite of our predators,” Joshua Corman, executive in residence for public safety and resilience at the Institute for Security and Technology (IST), told me last year. At the time, I was preoccupied with a…
Lire l’article complet Cybersécurité
An undercover Google analyst infiltrated a notorious supply-chain hacking gang
Before two of its alleged members were arrested and charged in Australia last month, the hacker group known as TeamPCP carried out a hacking spree unlike any other in history. It tainted hundreds of open-source programs with its malware, stole developer accounts to perpetuate that software supply-chain hacking, and even released a Dune-themed self-spreading worm to automate the process, ultimately breaching more than a thousand companies. Now Google’s threat intelligence group has revealed that…
Lire l’article complet Cybersécurité
Google confirms Gemini hacked into three companies during cybersecurity test months ago
Following a Wall Street Journal investigation, Google has confirmed that Gemini went rogue in May 2026, accessing the internet and breaching the security of three different companies. As AI continues to advance in its capabilities, we’re running into more cases of models going rogue. Perhaps the most infamous has been from OpenAI in the Hugging Face hack, but there plenty of other examples, including from Anthropic’s Claude. These incidents, in part, have led to…
Lire l’article complet Cybersécurité
Gemini went rogue, hacked three companies, and Google hid it
Google says that breaking containment and targeting real companies doesn’t constitute ‘misalignment.’ Google says that breaking containment and targeting real companies doesn’t constitute ‘misalignment.’ In May, Gemini broke containment and hacked three different companies, but Google didn’t disclose the incident until the Wall Street Journal approached the company. The hacks happened during a test of the model’s cybersecurity capabilities run by third-party Irregular, which was also involved in similar incidents involving Meta and OpenAI.…
Lire l’article complet Cybersécurité
The best way to check your PC for malware
If you suspect foul play on your PC, these scans will help you confirm it. When you think of a computer infected by malware, you might envision flashing pop-ups all over the screen or other obvious signs. And while these can happen today (like with ransomware), most modern computer attacks are more sinister and subtle. They want to avoid detection so they can capture your sensitive information and otherwise play the long game. Still,…
Lire l’article complet Cybersécurité
Google Gemini also escaped its testing environment and hacked three companies
The model escaped due to a misconfiguration by Google's testing partner, Irregular. Gemini escaped its testing environment, got access to the internet and hacked into three companies, Google has admitted to The Wall Street Journal. That scenario probably sounds familiar to you at this point, if you've even just glanced at AI news in recent months. Like what happened to OpenAI, Anthropic and Meta, Gemini also gained access to the internet due to a…
Lire l’article complet